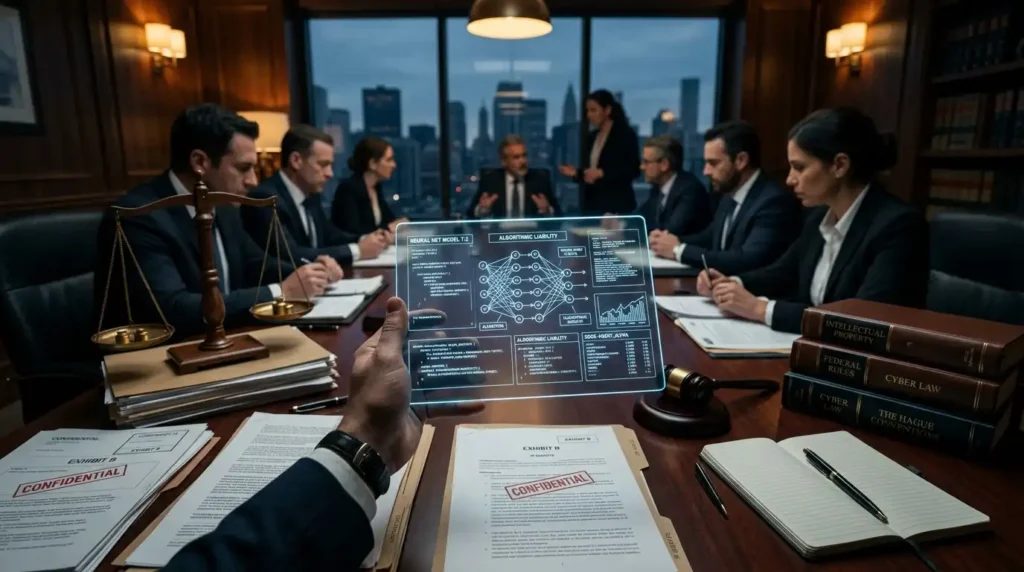
As artificial intelligence transitions from experimental software to enterprise-level operational infrastructure, global regulators are demanding unprecedented access to the inner workings of algorithmic systems. Leading this movement are regulatory frameworks such as the European Union’s flagship EU AI Act and a rapidly growing patch of U.S. state accountability laws. While these mandates aim to protect public safety, prevent algorithmic bias, and ensure transparency, they create an immediate legal headache for corporate counsel: How can companies comply with algorithmic disclosure requirements without forfeiting their most valuable trade secrets?
For technology developers and enterprise deployments, proprietary AI models, training datasets, weights, and fine-tuning pipelines represent core intellectual property (IP). Compelling the disclosure of these assets under regulatory oversight creates a high-stakes conflict between statutory compliance obligations and trade secret law.
The Scope of Emerging AI Transparency Mandates
Both global and regional statutory frameworks now mandate varying levels of technical disclosure from AI deployers and developers. These requirements focus on opening the “black box” of machine learning systems before and during commercial deployment:
- System Architecture & Weights: Detailed technical documentation outlining model architecture, hyperparameter configurations, and model training methodologies.
- Dataset Provenance & Summaries: Granular documentation detailing data sources, cleaning processes, and copyright-compliance summaries for training datasets.
- Algorithmic Impact Assessments (AIAs): Formal disclosures evaluating model bias, safety guardrails, failure conditions, and decision-making logic in high-risk applications (e.g., hiring, lending, healthcare, and law enforcement).
- Independent Third-Party Auditing: Mandated access for external red-teaming experts and regulatory bodies to test system parameters and verify safety claims.
While regulators maintain that these measures are essential for public accountability, the level of detail required often borders on providing a blueprint for reverse-engineering proprietary technology.
The Collision with Trade Secret Protection
Trade secret protection under frameworks such as the Uniform Trade Secrets Act (UTSA) and the federal Defend Trade Secrets Act (DTSA) in the United States relies on two key elements: the information must derive independent economic value from not being generally known, and the owner must exercise reasonable measures under the circumstances to maintain its secrecy.
Mandated algorithmic transparency threatens both elements of trade secret law:
1. The Risk of Regulatory Leaks and Public Disclosures
When enterprise developers submit technical documentation, source code summaries, or training data maps to regulatory oversight agencies or state repositories, those records risk becoming vulnerable to public records requests (such as state FOIA statutes) or administrative security breaches unless strict statutory exemptions are maintained.
2. Mandatory Third-Party Audits and Loss of Confidentiality Control
Allowing external auditors, government oversight panels, or plaintiff litigators to inspect model weights and training pipelines expands the circle of individuals with access to proprietary code. Even under strict non-disclosure agreements (NDAs), expanding system access increases the risk of inadvertent leaks or intellectual property exposure.
3. The Threat of Inadvertent IP Disclosure in Summary Summaries
Under regulations like Article 53 of the EU AI Act, general-purpose AI model providers must publish sufficiently detailed summaries of the content used for model training. Crafting a summary that satisfies regulatory oversight without revealing commercial strategies, proprietary data sets, or confidential source lists presents a delicate legal challenge.
Harmonizing Transparency Obligations with IP Defense
To navigate this legal conflict, corporate legal counsel and compliance teams must implement structured strategies that maintain statutory compliance while establishing robust defenses against trade secret loss.
1. Implement Tiered Data Disclosures
Rather than providing full raw code or unredacted training logs, organizations should develop multi-tiered disclosure documentation. High-level functional summaries and safety evaluation scores should satisfy public transparency requirements, while granular system architectures and sensitive weights are reserved exclusively for confidential, secure-environment regulatory review.
2. Assert Freedom of Information Act (FOIA) & Trade Secret Exemption Protections
When submitting mandatory compliance materials or Impact Assessments to state or federal regulatory bodies, explicitly mark proprietary technical details as “Confidential Business Information / Proprietary Trade Secret.” Ensure all regulatory filings include explicit administrative requests for exemption under applicable state and federal public disclosure laws.
3. Enforce Strict Auditor Confidentiality Protocols
When engaging independent red-teaming firms or external AI auditing vendors, ensure engagement contracts contain robust confidentiality clauses, limited-purpose use restrictions, strict data retention/destruction mandates, and prohibitions against using client data to train external models.
4. Document “Reasonable Measures” to Preserve Secrecy
Because trade secret enforceability requires proving active efforts to maintain confidentiality, document every safeguard applied during the regulatory disclosure process. Secure vault access, encrypted transmission logs, and access-tracked compliance portals demonstrate that disclosures were made under legal compulsion rather than voluntary forfeiture of secrecy.
Conclusion: The Path Forward for Corporate Legal Strategy
The conflict between corporate AI transparency mandates and trade secret law highlights an evolving tension in tech regulation. Companies can no longer treat AI models as unreviewable “black boxes,” nor can they expose their core intellectual property without risking significant commercial harm.
Proactive legal departments must integrate intellectual property counsel directly into the compliance lifecycle. By establishing clear disclosure boundaries, leveraging statutory trade secret exemptions, and enforcing strict regulatory data-handling agreements, enterprises can fulfill legal transparency requirements while preserving their most vital technological innovations.